
Scale your security
Secure every device effortlessly while ensuring compliance and growth.
Cover every gap
Gain visibility into devices and close security gaps before they become threats.
Protect Freelance & BYOD devices
Enable secure access for personal and external devices without adding complexity.
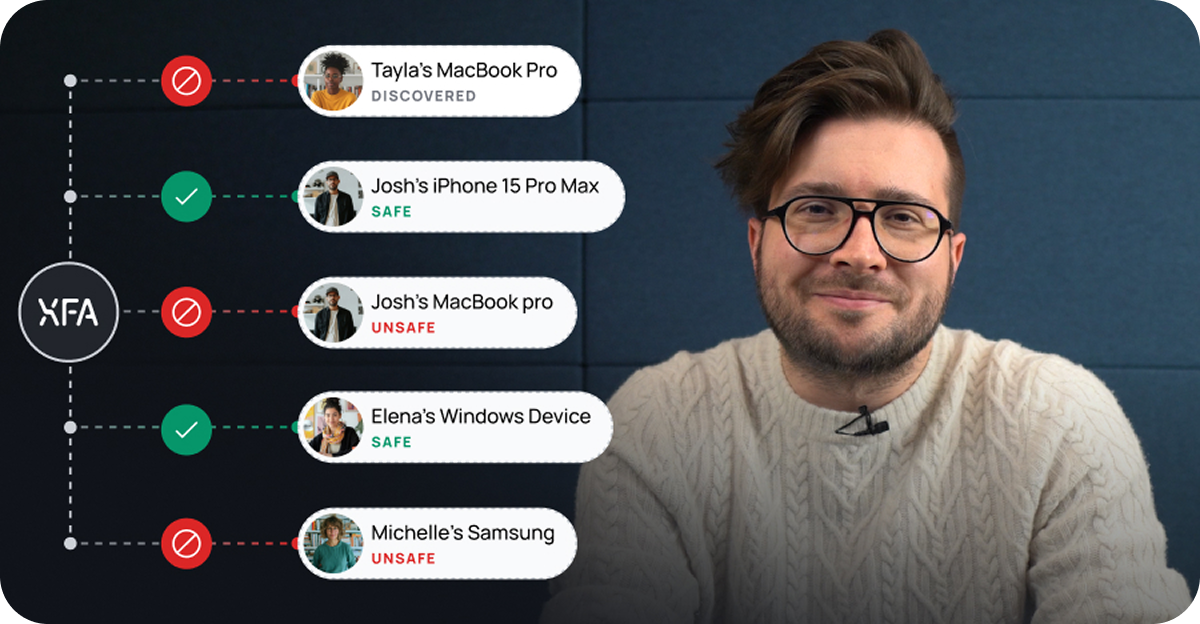
Device Security with XFA
Learn how XFA solves your device security issues.
Discovery
Gain visibility into all devices accessing your business platforms.
Awareness
Keep your team informed with real-time security alerts and insights.
Enforce
Ensure only compliant devices access your business data securely.
Silent MFA
Phishing-resistant MFA built into device trust.
Device Checks
See which security checks XFA can run on every device.
Download The Modern Device Security Guide
Curious what really works in device security?

A more efficient alternative to MDM
XFA secures every device used for work at login, without enrolling it or taking control of it. Built for companies with a mixed device fleet: company-owned, personal and contractor devices, on any operating system.
See XFA next to your MDM
We can help you compare based on your team's needs.
Securing devices for leading organizations like




What is XFA?
XFA is the device security solution that identifies every device used by people in your organization, informs users about risks, and verifies compliance with your security policy at login, without needing to manage or control the device. It runs standalone: no identity provider migration, no manual device enrollment.
What is an MDM?
An MDM (Mobile Device Management) is a tool IT teams use to manage company devices centrally. To secure a device, the MDM first needs to enroll it and take control of it, then IT uses it to push applications, updates and compliance checks onto each enrolled device. We will compare this traditional device security approach with XFA.
XFA vs MDM, feature by feature
 Included
 Not included
XFA
MDM
Security Checks
Blocks non-compliant devices at login
 Only in combination with Conditional Access.
Made for self-install
Device and User Support
Works for contractor devices and BYOD
An MDM takes full control of the device, so contractors and employees often refuse to enroll their own devices for privacy reasons.Never takes control of the device
Enrolling a device in an MDM gives IT management rights over it, including remotely wiping company data or the whole device.Discovers every device through SSO, no app installed
An MDM only sees enrolled devices, so personal devices used for work stay invisible.Ecosystem
Supports any operating system
Most MDMs focus on one platform family and often don't support Linux and mobile devices.No identity provider migration needed
Blocking devices at login usually depends on the MDM vendor's own identity platform, such as Microsoft Entra ID for Intune.Why choose XFA over an MDM solution?
Three differences that decide it for most teams.
See the difference in your own environment.
Start free.
Simple per-user pricing with unlimited devices, and no migration from your current setup required.
What our customers say
"I think it's a good balance between being lightweight, non-intrusive, and transparent. Transparent in the sense of what you are looking at. The only way for me to get adoption was actually giving people access to the dashboard and showing what I'm looking at. Other solutions we tested didn't make it that transparent."
Read the full testimonial →
 4.9/5 on G2
Compare XFA to other tools
Curious how XFA stacks up against other device security and identity tools? Explore the comparisons to see how we secure your modern workforce without the friction of invasive management profiles.