The hidden risk in your device fleet: What IT teams are missing in endpoint security
Why endpoint visibility is a 2025 priority
In most organizations, IT teams sometimes have a dangerously misleading sense of control thanks to tools like MDMs. However, most traditional solutions like that don’t account for the entire device landscape used in hybrid work.
The reality? A big number of devices used for work remain invisible to traditional MDM and endpoint protection systems. They represent one of the biggest modern security blind spots. Those include:
- Freelancers and contractors logging in from unregistered devices;
- Employees switching between BYOD and company-issued devices;
- Unmanaged Linux, macOS, and Windows devices;
- Personal mobile devices;
- Remote teams working from a mix of secure and outdated endpoints.
These blind spots aren’t hypothetical. They’re active vulnerabilities that put compliance and business continuity at risk.
MDM coverage isn’t enough anymore
Even top-tier platforms don’t guarantee full coverage. Why?
- MDM platforms assume full control, which is a poor fit for BYOD;
- They often miss unregistered, unmanaged, or noncompliant devices;
- Coverage is inconsistent across operating systems;
- Setup and maintenance require serious IT overhead.
This creates gaps in your zero trust architecture.
The data doesn’t lie
An internal XFA study across dozens of organizations revealed:
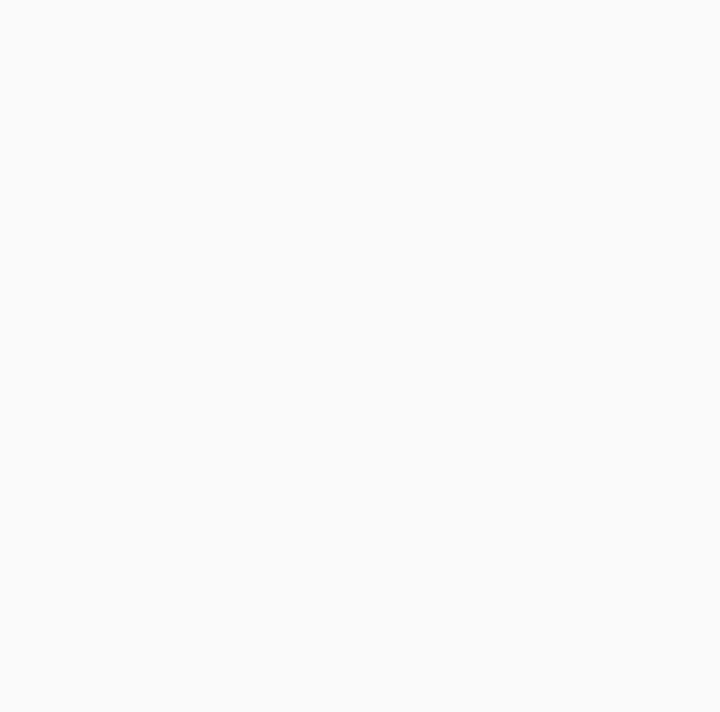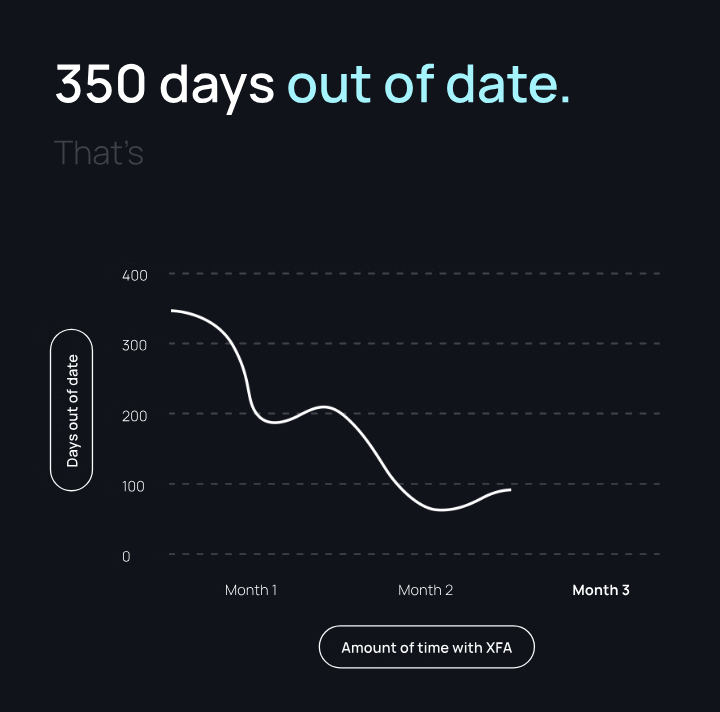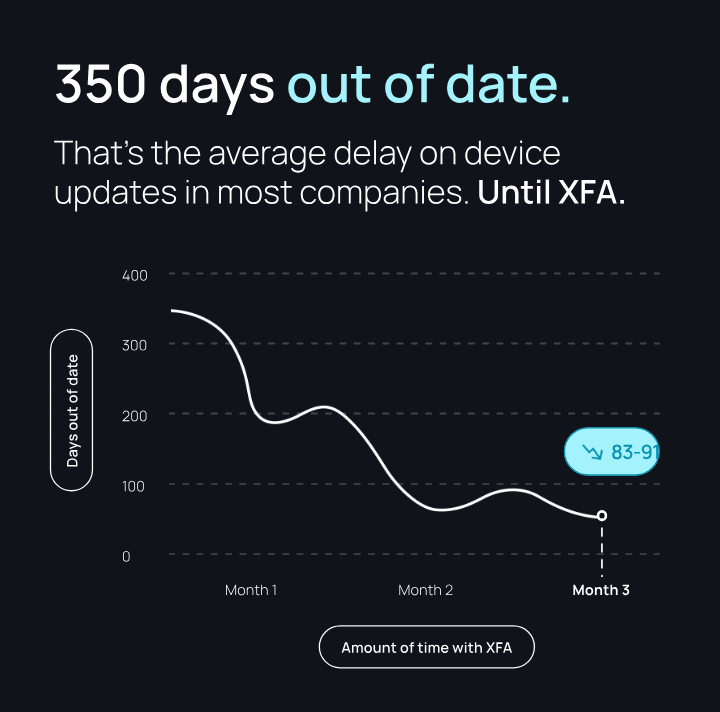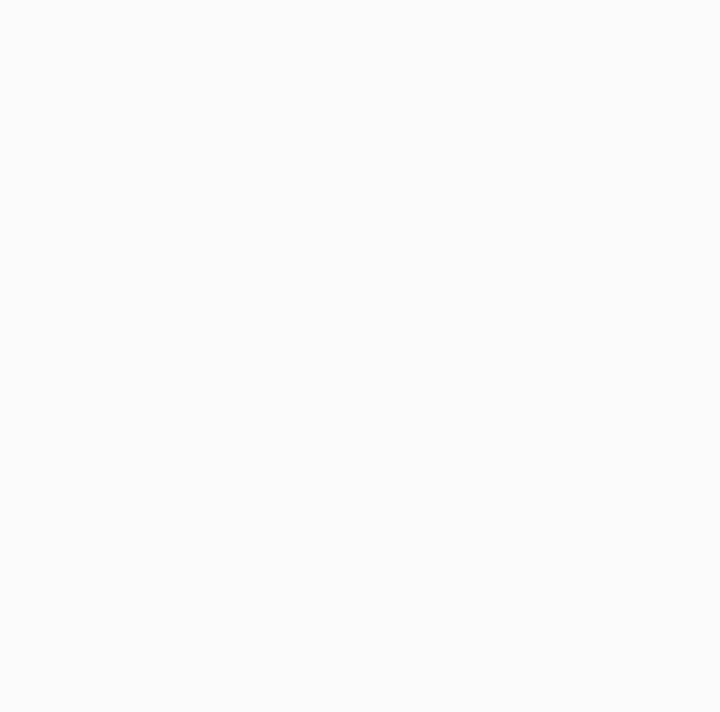
The average device used for work is 350 days behind on updates.
This means:
- Almost a year without security patches;
- Nearly 12 months of exposure to browser exploits, OS vulnerabilities, and unmonitored endpoints;
- Compliance risks with frameworks like SOC 2, ISO 27001, and NIS2.
Even companies with the best EDR software and endpoint protection services are leaving themselves vulnerable, simply because they can’t see every device used for work.
The impact of full-fleet device trust
XFA is built for today’s hybrid and privacy-first workforce. It helps security teams see beyond MDM without taking control over devices.
Organizations that adopt XFA typically reduce device outdatedness from:
350 days → 30–60 days within the first 3 months.
Ready to see what MDM can’t? Talk to our team to explore XFA’s modern alternative to traditional tools.